Stack Trace
Stack traces are useful for debugging vulnerable applications with a great degree of accuracy. The output can however be quite verbose, and the stack trace feature does not apply to all rule types.
When the RASP Java Agent detects an attack, if the Stack Trace feature is turned on, RASP Java Agent can provide a full stack trace to pinpoint the exact line of code that is vulnerable.
The following rule models support the stack trace feature:
- Cross-site request forgery (CSRF)
- Cross-site scripting (XSS)
- Deserialization of untrusted data
- DNS lookups
- FileSystem read/write
- Improper input validation
- Library loading
- Open redirection
- Path traversal
- Process forking (command injection)
- Reflect
- Socket - accept
- Socket - bind
- Socket - connect
- SQL injection
- XML external entity (XXE)
The stack trace feature toggle is available for each of the above rules within the Rules Wizard in the Security events section, if the rule supports it. If the Disable security events option is selected in this section, then the stack trace option will be disabled and unavailable.


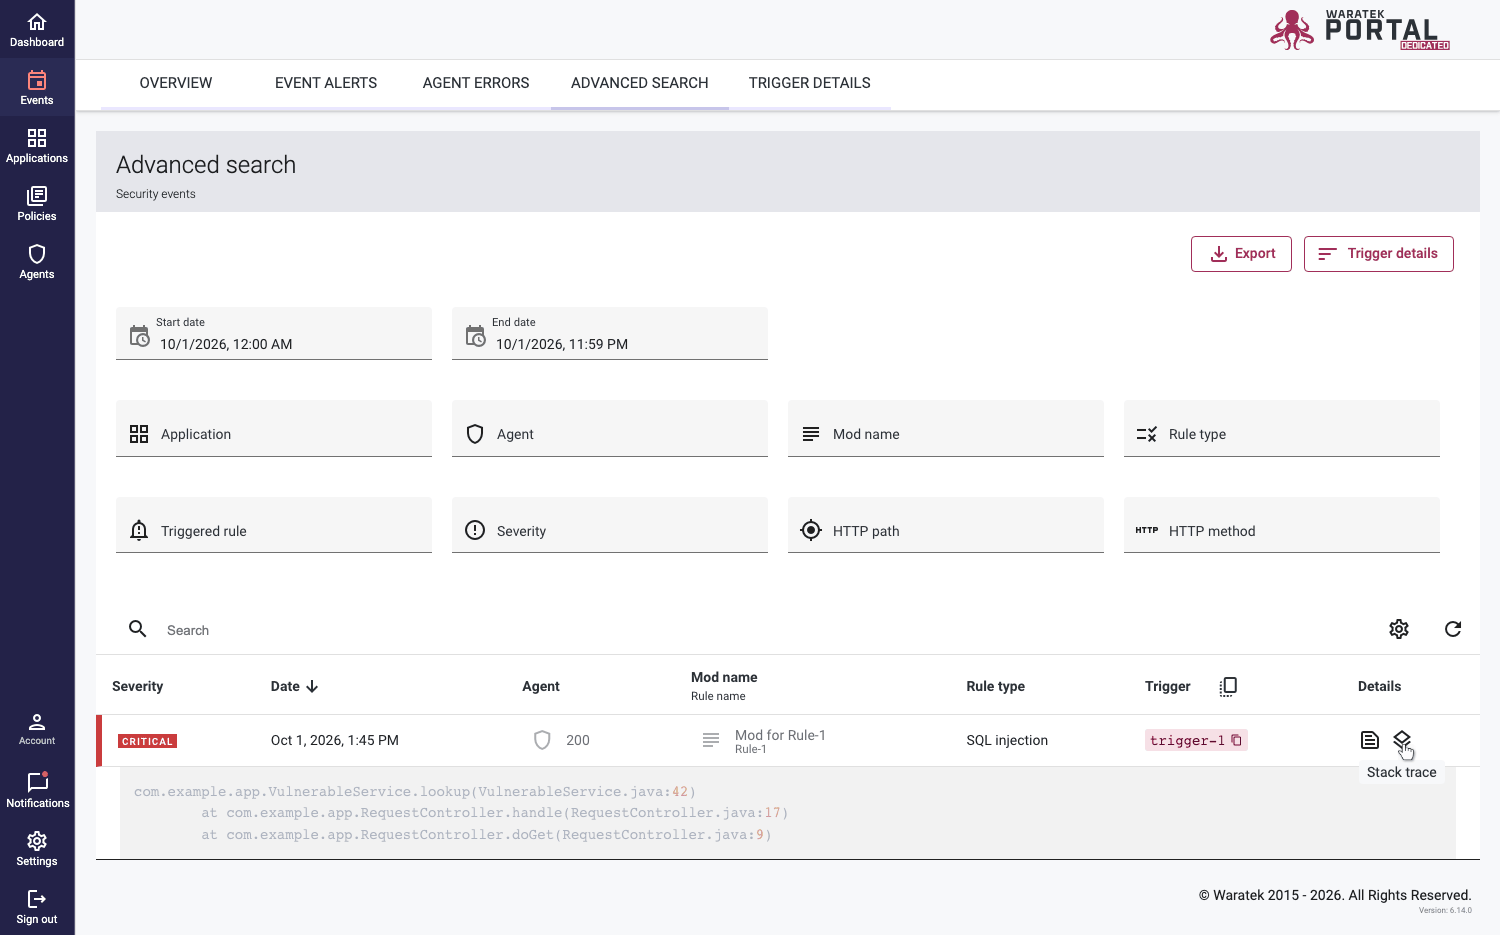
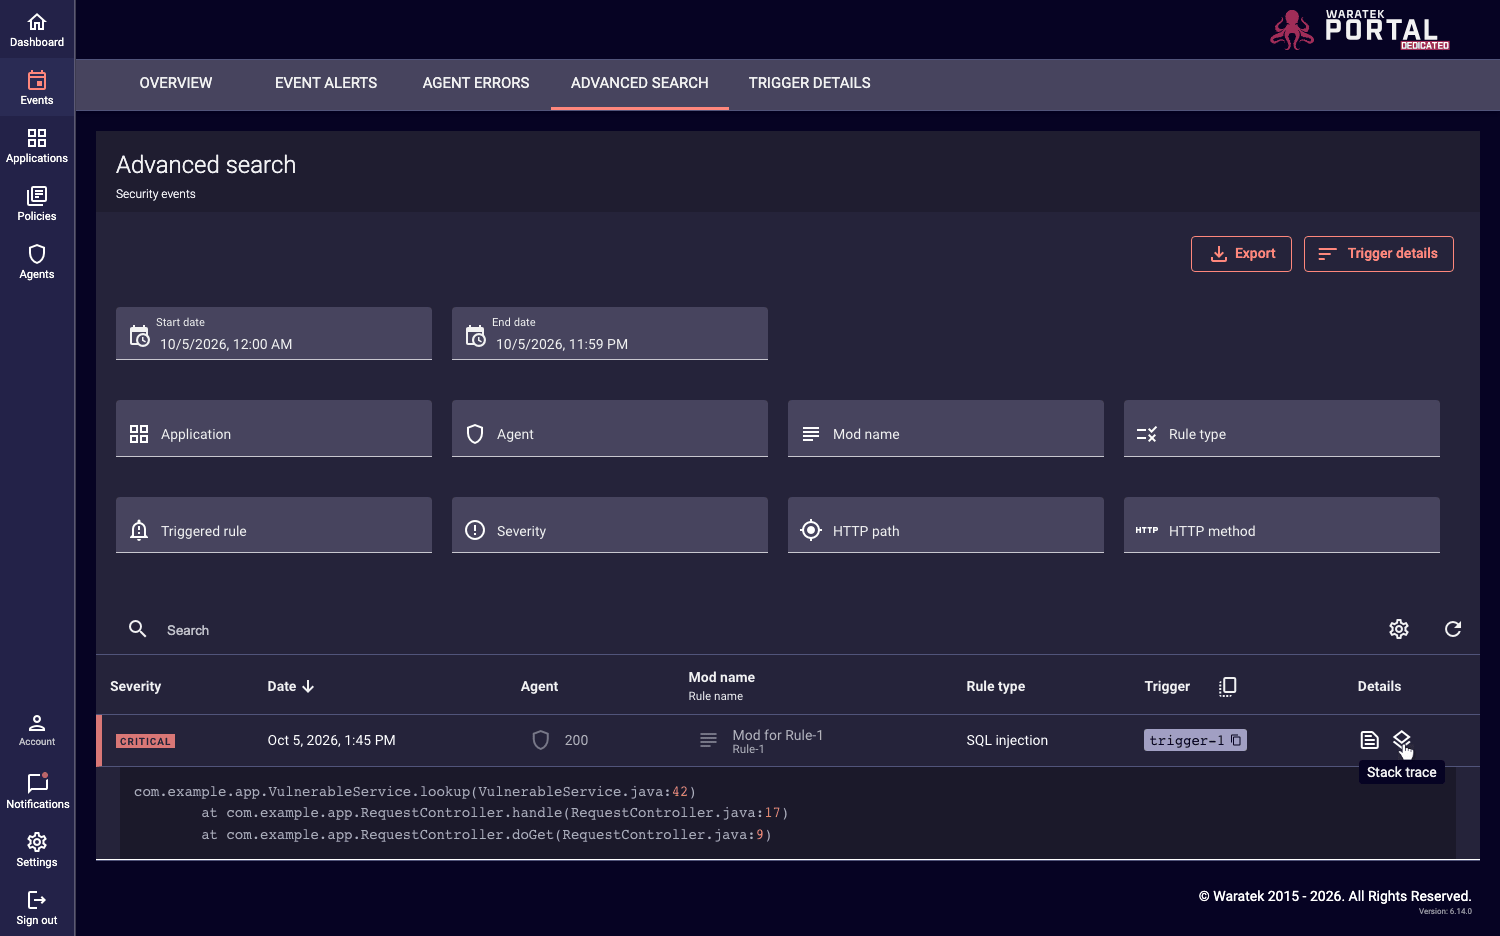
When a rule is triggered and a stack trace is created, a Stack Trace icon  will appear in the Details column, next to the Details icon
 , for the individual events in the Advanced Search table. When you click on the Stack Trace icon on an event row, the stack trace will appear in an expanded view below the row, with the standard event log details included.